We build control environments, then help you prove them
Since 2014, Vyapari Solutions has delivered over 1,200 audits and assessments across 38+ countries — with a 96% first-attempt certification rate and a rule we do not bend: we never certify our own clients.
4.9/5 average client rating · 1200+ engagements delivered
Compliance became a paperwork industry. We think that is the problem.
Most organisations we meet have already bought a policy pack. It sits in a shared drive, nobody reads it, and it fails at the first evidence request because it describes a company that does not exist.
Our position is simple: a management system is only worth building if the people who run the business would keep running it after the auditor leaves. That means designing controls around the tools your teams already use, mapping evidence to systems that already produce it, and cutting everything that exists purely to be shown to an auditor.
It also means being honest about scope. We have talked clients out of frameworks they did not need more often than we have upsold them, because a certificate nobody asked for is an expensive way to feel prepared.
- Accredited auditors, not resellers
- Fixed-fee engagements, zero surprise costs
- Evidence-first methodology mapped to every clause
- Single team for cyber security and ISO standards
Vyapari Solutions at a glance
| Founded | 2014 |
|---|---|
| Audits delivered | 1,200+ across 38 countries |
| First-attempt pass rate | 96% |
| Frameworks covered | 8 cyber security & regulatory, 12 ISO standards |
| Offices | New Delhi, India |
| Engagement model | Fixed fee, fixed timeline, named delivery team |
Four commitments we hold to on every engagement
Evidence over paperwork
We do not sell template packs. Every control is mapped to a real artefact produced by a real system in your environment.
Independence, always
We prepare and we audit internally — we never certify our own clients. That separation is what makes the certificate mean something.
Your team, not ours, operates it
A management system that only we can run collapses at the first surveillance audit. We build for handover from day one.
Fixed fee, no change orders
The quote lists scope, sites, audit days and every deliverable. If we scoped it wrong, that is our problem, not your budget.
Accreditations, empanelments and personal certifications
 NABCB accredited partners
 IAF MLA recognised
 CERT-In methodology
 PCI DSS QSA-led
 ISO 27001 certified team
Lead auditors (IRCA / Exemplar)
Licensed CPA firm network
CMMI certified appraisers
What sits behind the delivery team
Certified assessors
Lead auditors for ISO 27001, 9001, 14001, 45001, 22000 and 13485, QSA-led PCI DSS practice, OSCP and CREST-aligned testers, and certified privacy professionals.
Sector benches
Dedicated delivery teams for BFSI, food, energy, technology and data centres, construction, healthcare and railways.
Global delivery
Engagement teams in India and the UAE serving 38+ countries, with remote audit delivery accepted by all major accreditation bodies.
Training practice
Lead auditor, internal auditor, awareness, secure development and incident response training, delivered on-site or remotely.
Advisory retainers
Fractional CISO, DPO-as-a-service, EU/UK representative appointment and ongoing surveillance readiness support.
Incident support
A 24/7 escalation line for retainer clients covering CERT-In reporting, breach notification and forensic preservation.
Delivered from India and the UAE, accepted worldwide
Remote audit delivery is accepted by every major accreditation body, and IAF MLA recognition means the certificate travels with you into new markets.
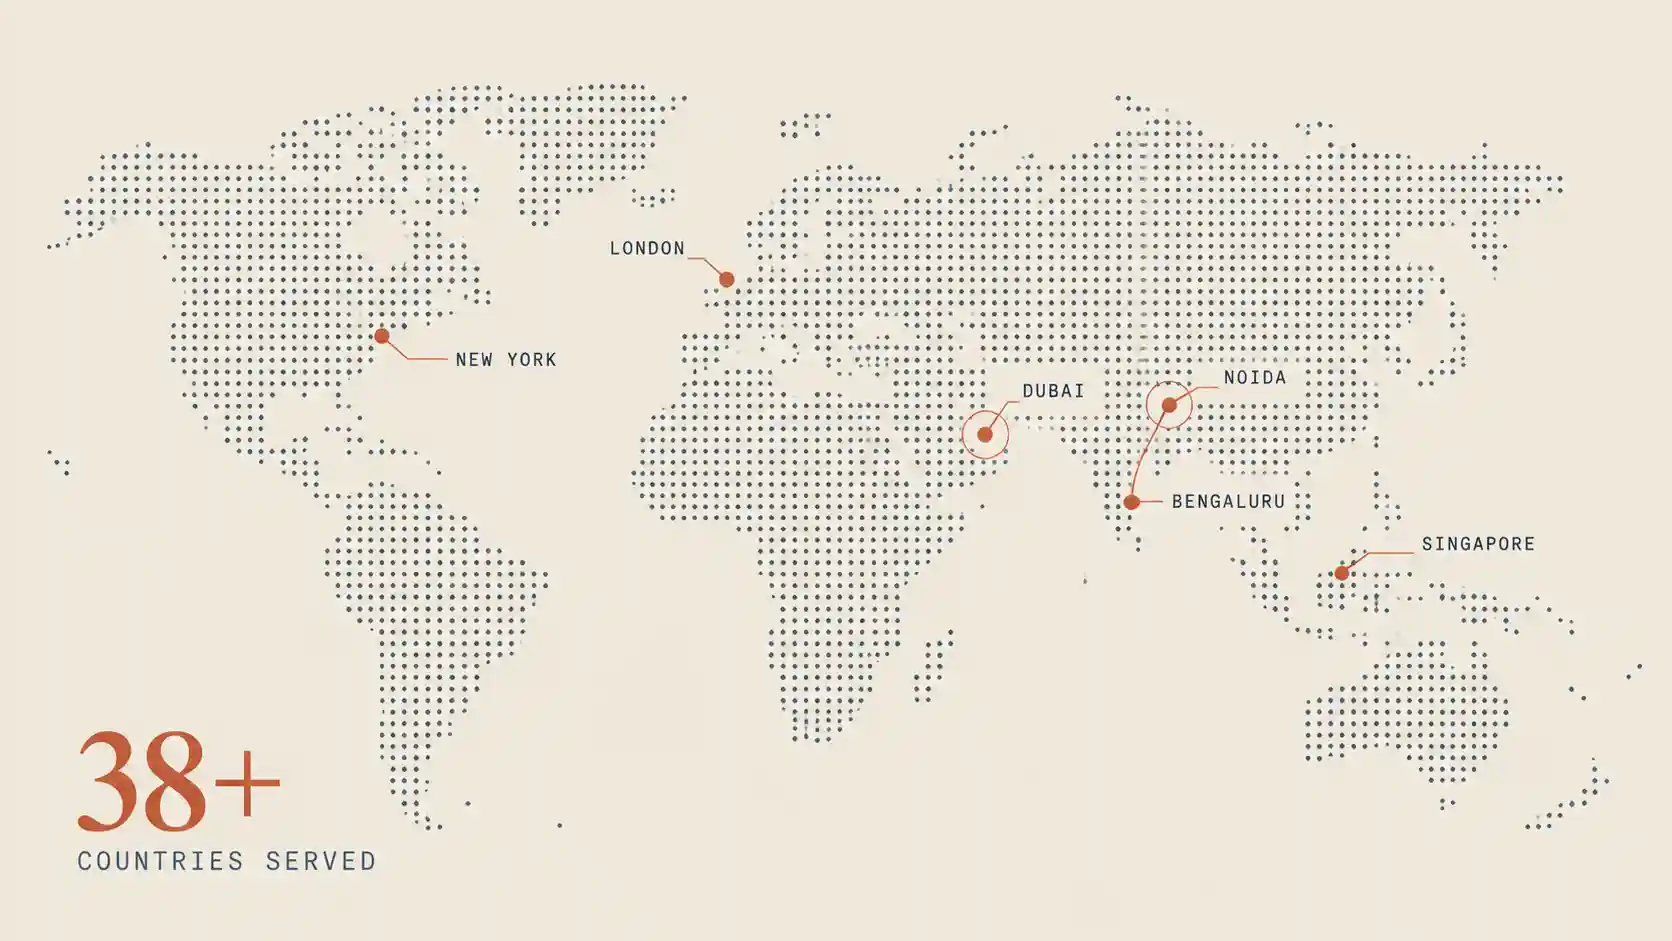
Delivery hubs in India and the UAE, remote engagement teams across 38+ countries.
What working with us actually looks like
Scope & gap assessment
We map assets, data flows, applicable clauses and regulatory triggers, then quantify the gap in a board-ready report.
Design & remediation
Policies, procedures, risk register and technical controls are built with your teams — not handed over as a template pack.
Internal audit & readiness
A full dry-run audit with evidence sampling, management review and corrective actions before the certification body arrives.
Certification & surveillance
We coordinate the accredited audit, close findings and keep you audit-ready through annual surveillance cycles.
About Vyapari Solutions — FAQ
We run multi-disciplinary delivery pods rather than a large generalist bench — typically a lead assessor, a technical specialist and a documentation lead per engagement, backed by a sector partner. You always know exactly who is working on your project.
No. Delivery is performed by our own assessors under signed NDAs. Where a certificate must be issued by an accredited certification body or a licensed CPA firm, that is a separate independent engagement and we tell you exactly who it is with.
Surveillance audits arrive every year, and systems drift. Most clients move to a light retainer covering internal audit, management review facilitation, evidence health checks and surveillance preparation — which is far cheaper than remediating a suspended certificate.
Yes, frequently. We are often brought in for a specific technical scope — VAPT, a PCI DSS scope reduction, a DPIA programme — alongside an incumbent partner handling the wider management system.
Still not sure what applies to you?
Ask an assessor directly — we answer scoping questions before anyone talks about a fee.
A 30-minute call costs nothing and usually saves months
Bring the security questionnaire, the tender clause or the regulator letter that started this. We will tell you what it actually requires.