Compliance that protects revenue, not just records
Vyapari Solutions takes you from gap assessment to certificate — SOC 2, PCI DSS, DPDP, VAPT, CERT-In, HIPAA, GDPR, CMMI and the full ISO management system family — with one accountable team and a fixed timeline.
4.9/5 from compliance leads at 1200+ engagements
- ISO 27001Stage 2 closed · 0 major NCs
- SOC 2 Type IIEvidence window · day 62 of 90
- VAPT retest4 high findings closed
Illustrative posture view. Yours is built from your own evidence, in your own tools — we do not ask you to move anything into ours.
Frameworks we deliver end to end
Four practices, one accountable team
Most organisations buy compliance in fragments and pay for the same evidence three times. Vyapari Solutions runs security, standards and sector advisory as a single programme.
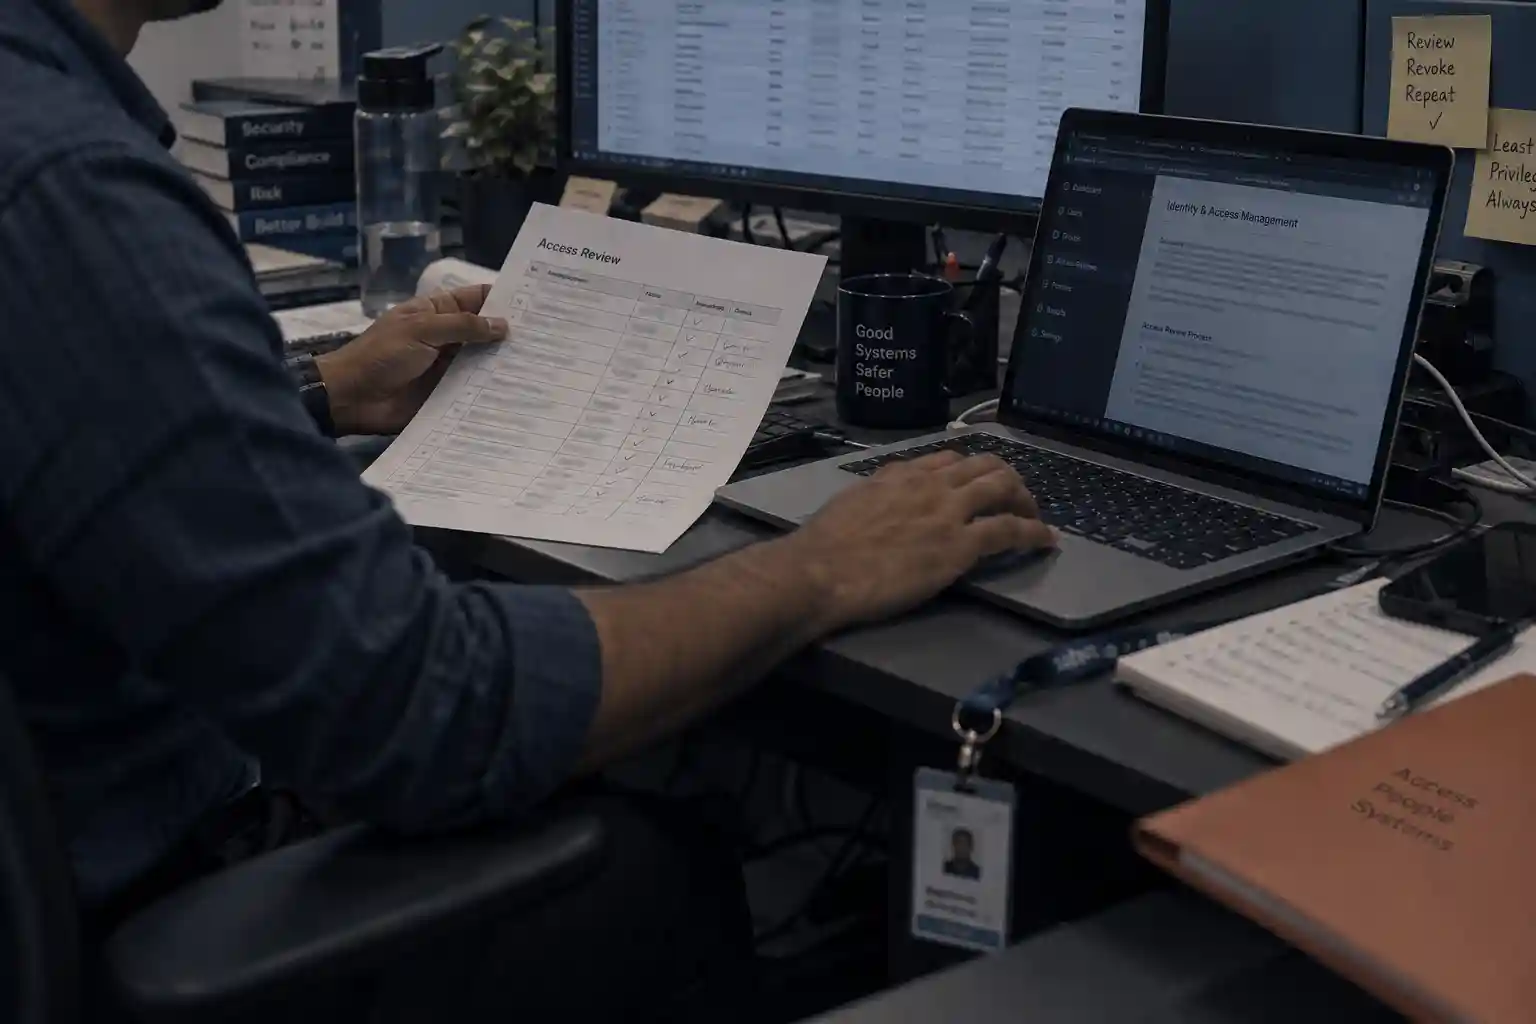
Cyber Security & Regulatory
SOC 1/2, PCI DSS, DPDP Act, VAPT, CERT-In audits, HIPAA, GDPR and CMMI appraisals delivered by certified assessors.
Learn more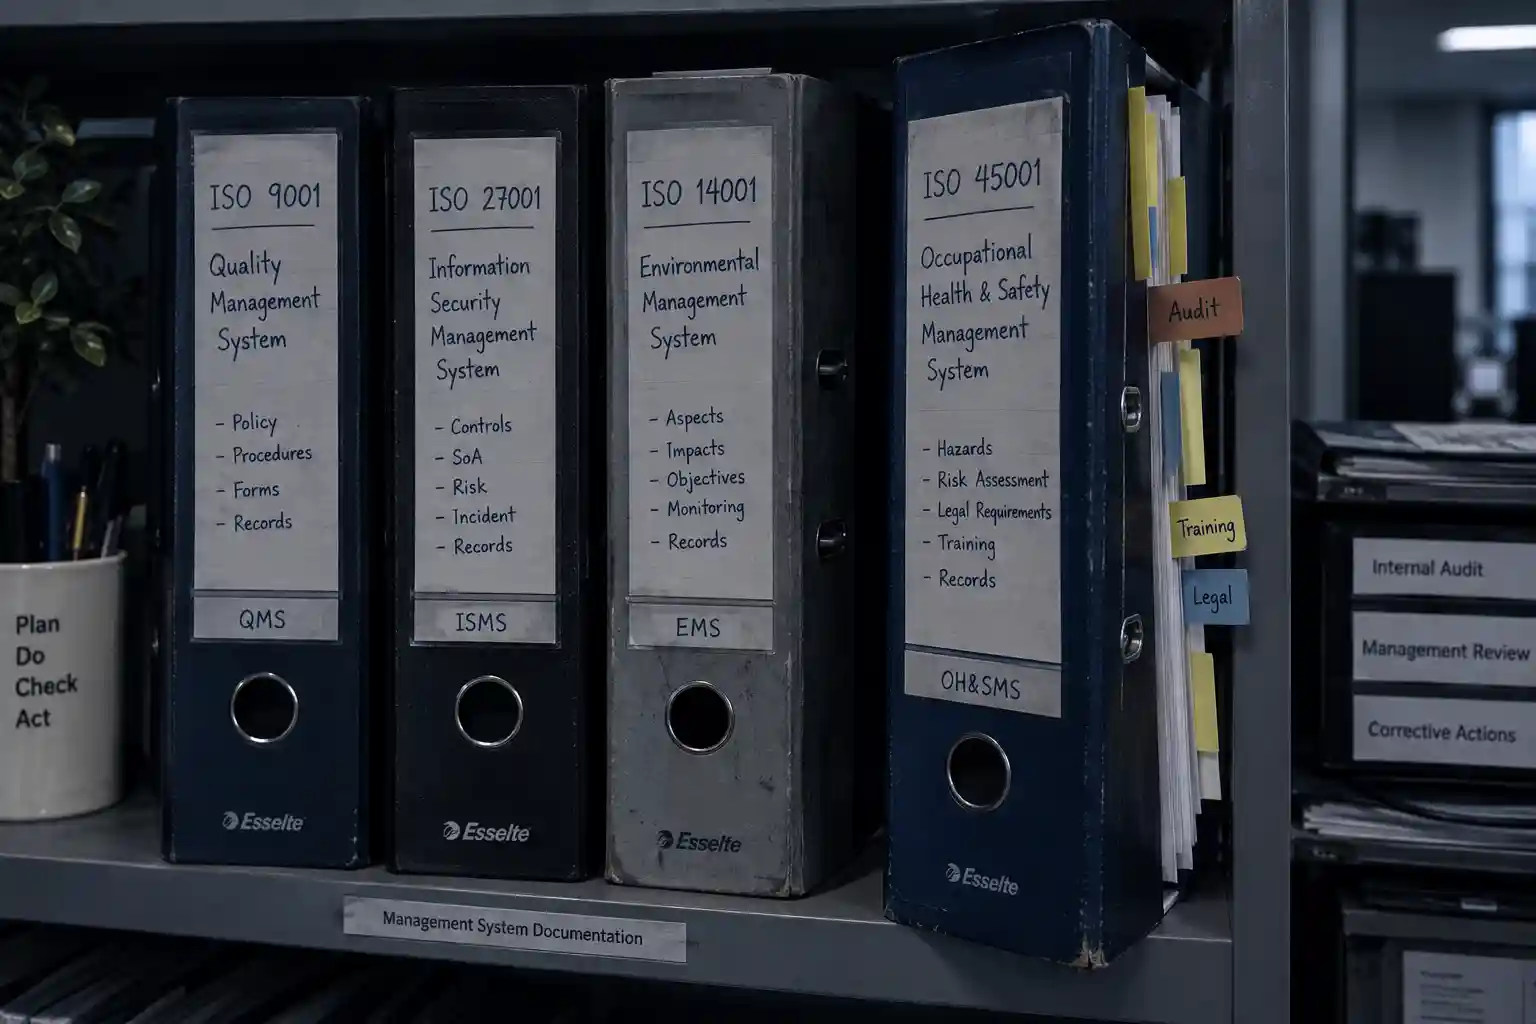
Standard Compliance
Twelve ISO management system standards plus NABCB-aligned certification support, from documentation to surveillance audits.
Learn more
Sector Expertise
Auditors who already speak your language — BFSI, food, energy, data centres, construction, healthcare and railways.
Learn more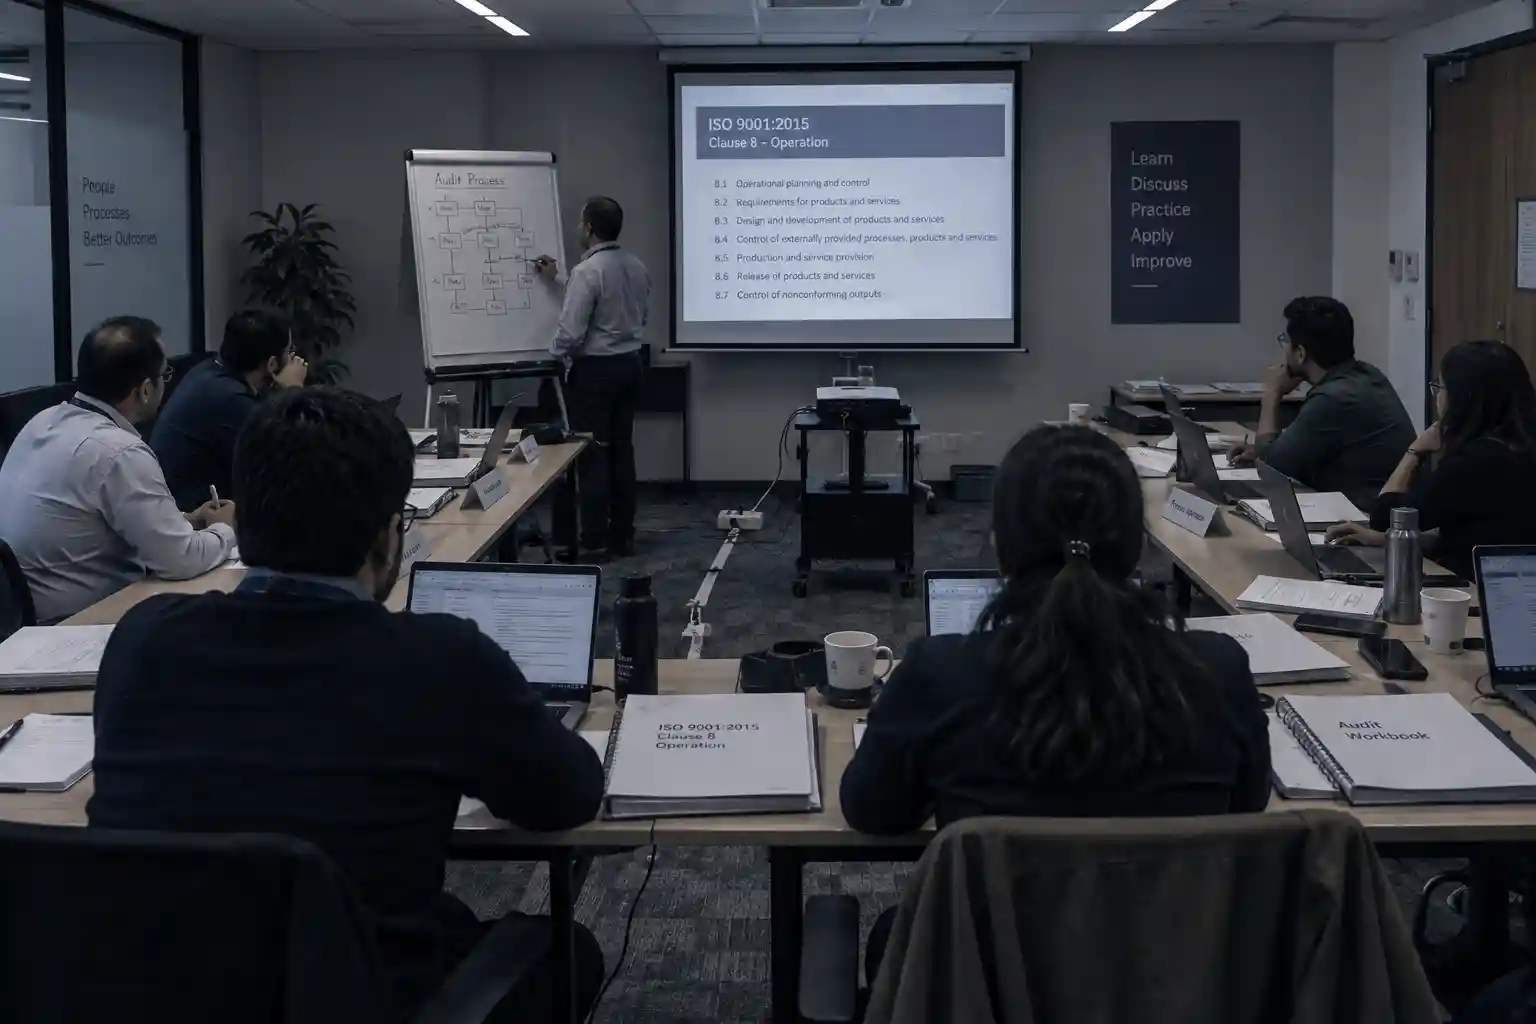
Training & Advisory
Lead auditor, internal auditor, awareness and secure-development training, plus fractional CISO and DPO advisory.
Learn moreFewer vendors, fewer surprises, one evidence set
The cost of compliance is rarely the certificate — it is the third time your engineers export the same access review for a different auditor.
One programme instead of four vendors
Security testing, ISO implementation, privacy and sector advisory run off one control library and one project plan — so nobody hands you a gap and calls it someone else’s scope.
- One evidence request list for your engineers
- One reporting line, one weekly status
- One fixed fee agreed before kick-off
of controls shared across frameworks
ISO 27001 and SOC 2 overlap almost entirely. We test once and report many ways.
from kick-off to gap report
A board-ready gap analysis with owners, effort and a dated remediation plan.
Auditors see your systems, not our templates
Every control is mapped to a real artefact from your stack — a ticket, a log, a config export — so audit day has nothing left to discover.
frameworks under one roof
Eight cyber and regulatory practices plus twelve ISO management system standards.
See all frameworks Supportincident response desk
CERT-In reporting clocks start in six hours. Someone picks up at 3am.
Cyber servicesAudits and attestations your buyers already trust
Certified assessors, evidence-first methodology, and reports formatted for the regulator, bank or enterprise customer who asked for them.
SOC 1 & SOC 2
AICPA Trust Services Criteria
Trust Services readiness and Type I / Type II attestation support.
Details
PCI DSS
PCI DSS v4.0.1 · QSA-led
QSA-led v4.0.1 gap assessment, remediation, RoC and SAQ support.
Details
DPDP Act 2023
Digital Personal Data Protection Act, 2023
India’s privacy law: consent, notices, DPO and breach readiness.
Details
VAPT
OWASP · NIST SP 800-115 · PTES
Network, web, mobile, API, cloud and red team testing.
Details
CERT-In
CERT-In Directions · 70B
CERT-In directions readiness, security audit and log compliance.
Details
HIPAA
Privacy · Security · Breach Notification Rules
US healthcare privacy and security rule compliance for PHI.
Details
GDPR
EU GDPR · UK GDPR
EU/UK data protection: DPIA, DSR, transfers and DPO services.
Details
CMMI Level Audit
CMMI V3.0 · Benchmark Appraisal
CMMI V3.0 maturity level appraisal readiness, Level 2 to 5.
DetailsTwelve ISO standards, one integrated management system
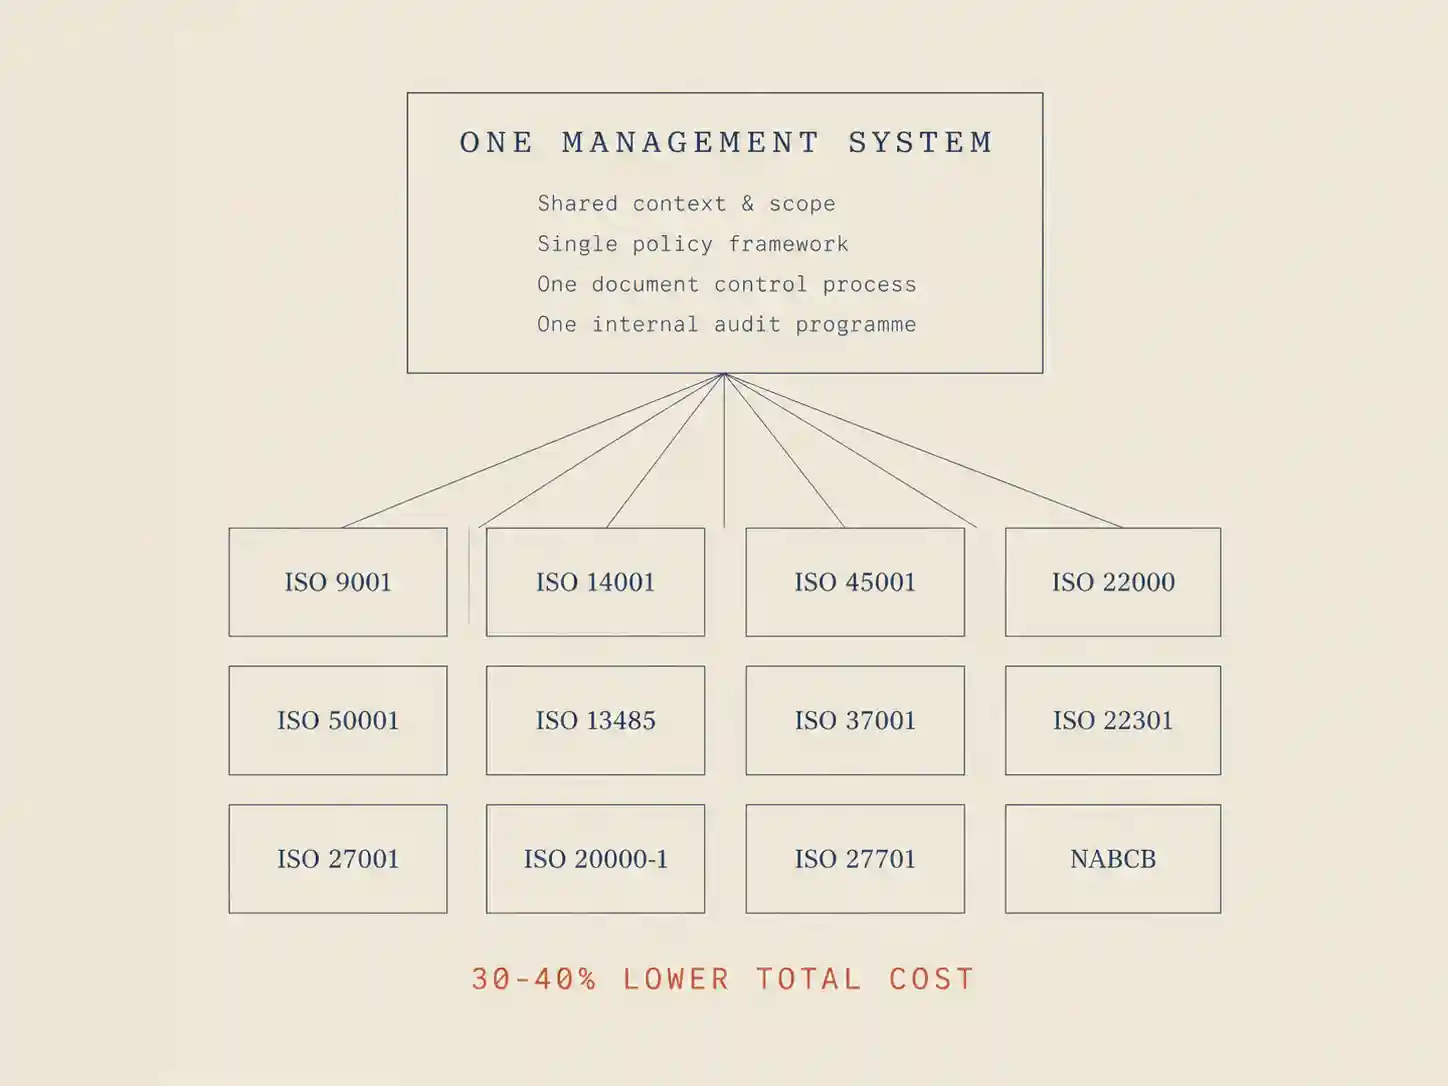
Certifying separately means three context analyses, three audit programmes and three sets of audit days every year. We build one system that satisfies all of them, then coordinate a single accredited audit.
- Shared context, policy, document control and internal audit programme
- One management review covering every standard in scope
- Typically 30–40% lower total cost than separate certifications
- NABCB and IAF MLA accredited certification bodies only
 All twelve standards
The difference between a certificate and a control environment
Evidence-first, not template-first
Every control is mapped to real artefacts from your stack, so audit day has no surprises.
Certification in 8–14 weeks
Parallel workstreams for documentation, remediation and internal audit compress the calendar without cutting scope.
One framework, many certificates
Shared controls are tested once and reused across SOC 2, ISO 27001, DPDP and GDPR to cut cost by up to 40%.
Your data never leaves your control
Assessments run inside your environment with least-privilege access and signed NDAs for every engineer.
No — and that is deliberate. Accreditation rules require independence between the consultant and the certification body.
Why we do not issue the certificate ourselves
What changes when the same team owns the whole programme
Six places where compliance projects usually go sideways, and how our engagements are structured to avoid each one.
-
Scope definition
Fixed in writing after a free scoping call — sites, headcount, audit days, deliverables
UsuallyLoosely worded, then re-scoped by change order mid-project
-
Documentation
Written against your real processes and signed off by the process owner
UsuallyGeneric template pack with your logo dropped in
-
Evidence collection
Collected once, mapped to every framework in scope
UsuallyRe-requested separately for each certificate
-
Who runs the audit
Independent accredited body — we prepare you and coordinate them
UsuallySame firm consults and "certifies", which breaks accreditation rules
-
After the certificate
Surveillance calendar, internal audits and refreshers included for the cycle
UsuallyEngagement ends the day the certificate is issued
-
Pricing
One fixed fee, agreed before work starts
UsuallyDay-rate that grows with the project
From first call to certificate in four stages
Every engagement is fixed-fee and time-boxed. You get the week-by-week plan before you sign anything.
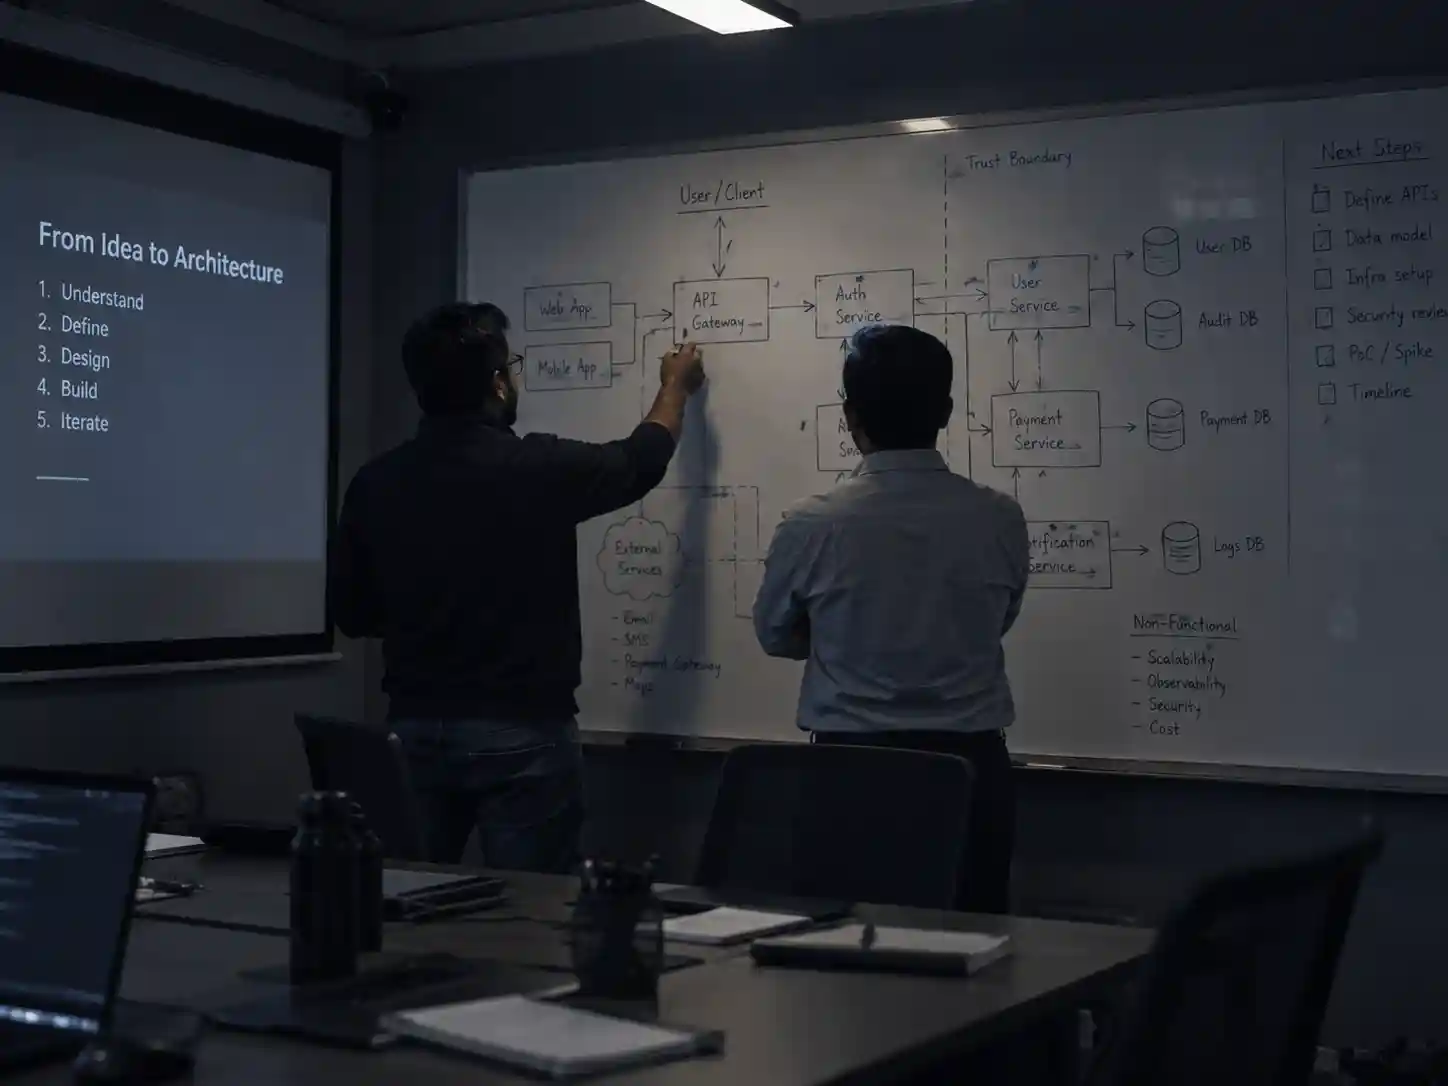
Scope & gap assessment
We map assets, data flows, applicable clauses and regulatory triggers, then quantify the gap in a board-ready report.
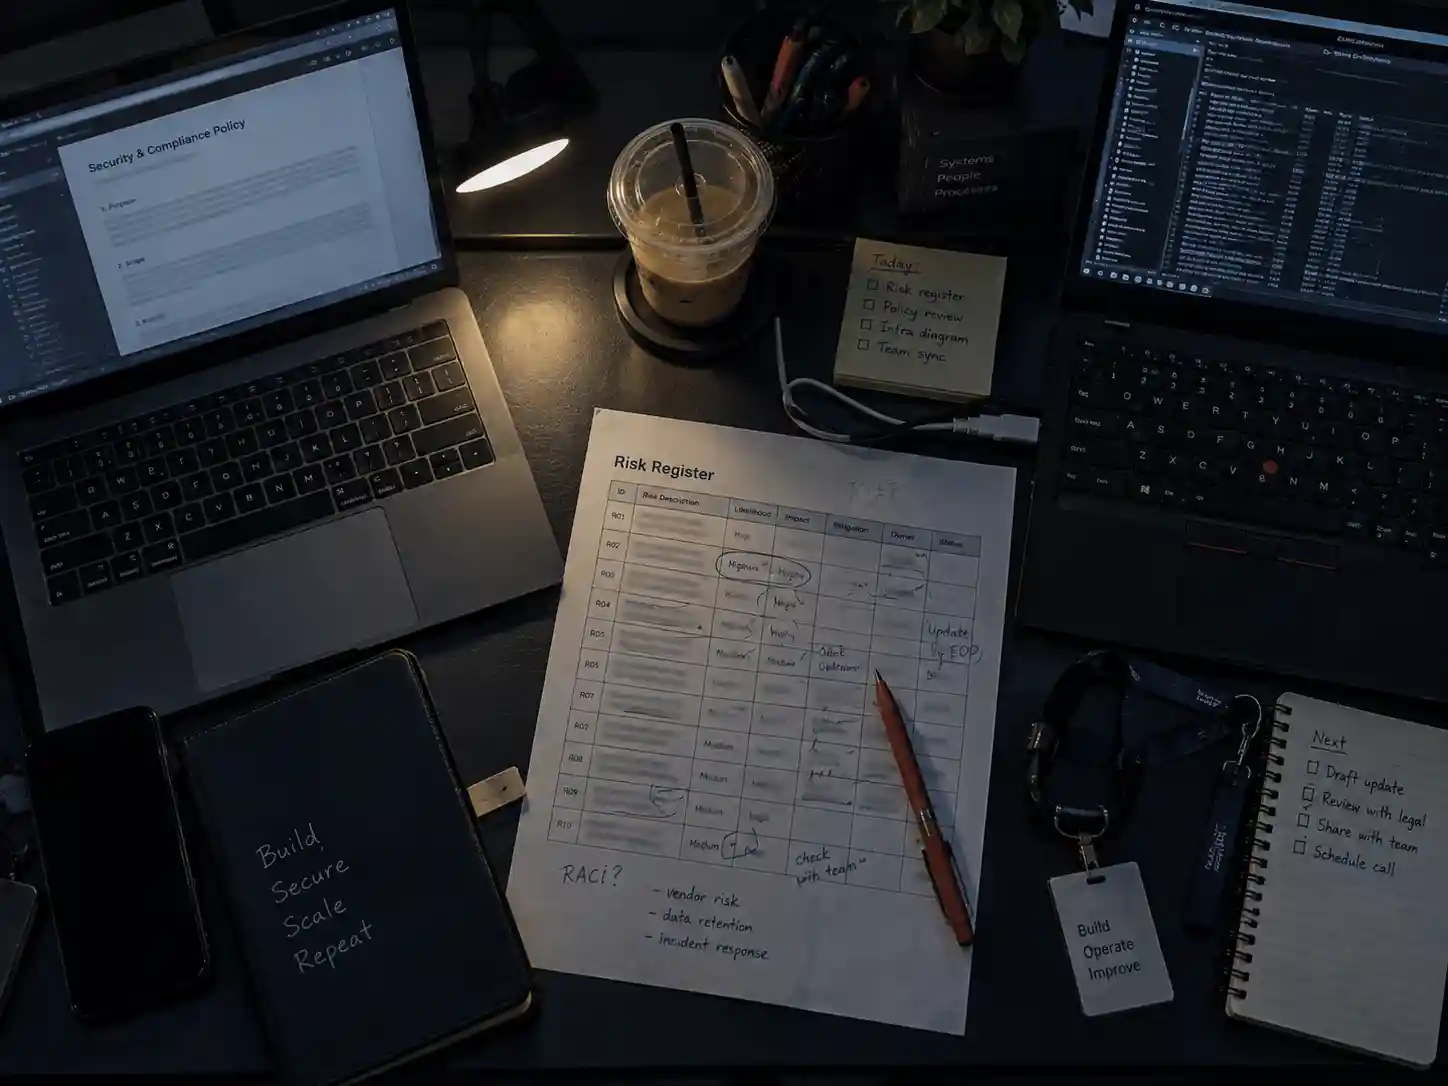
Design & remediation
Policies, procedures, risk register and technical controls are built with your teams — not handed over as a template pack.
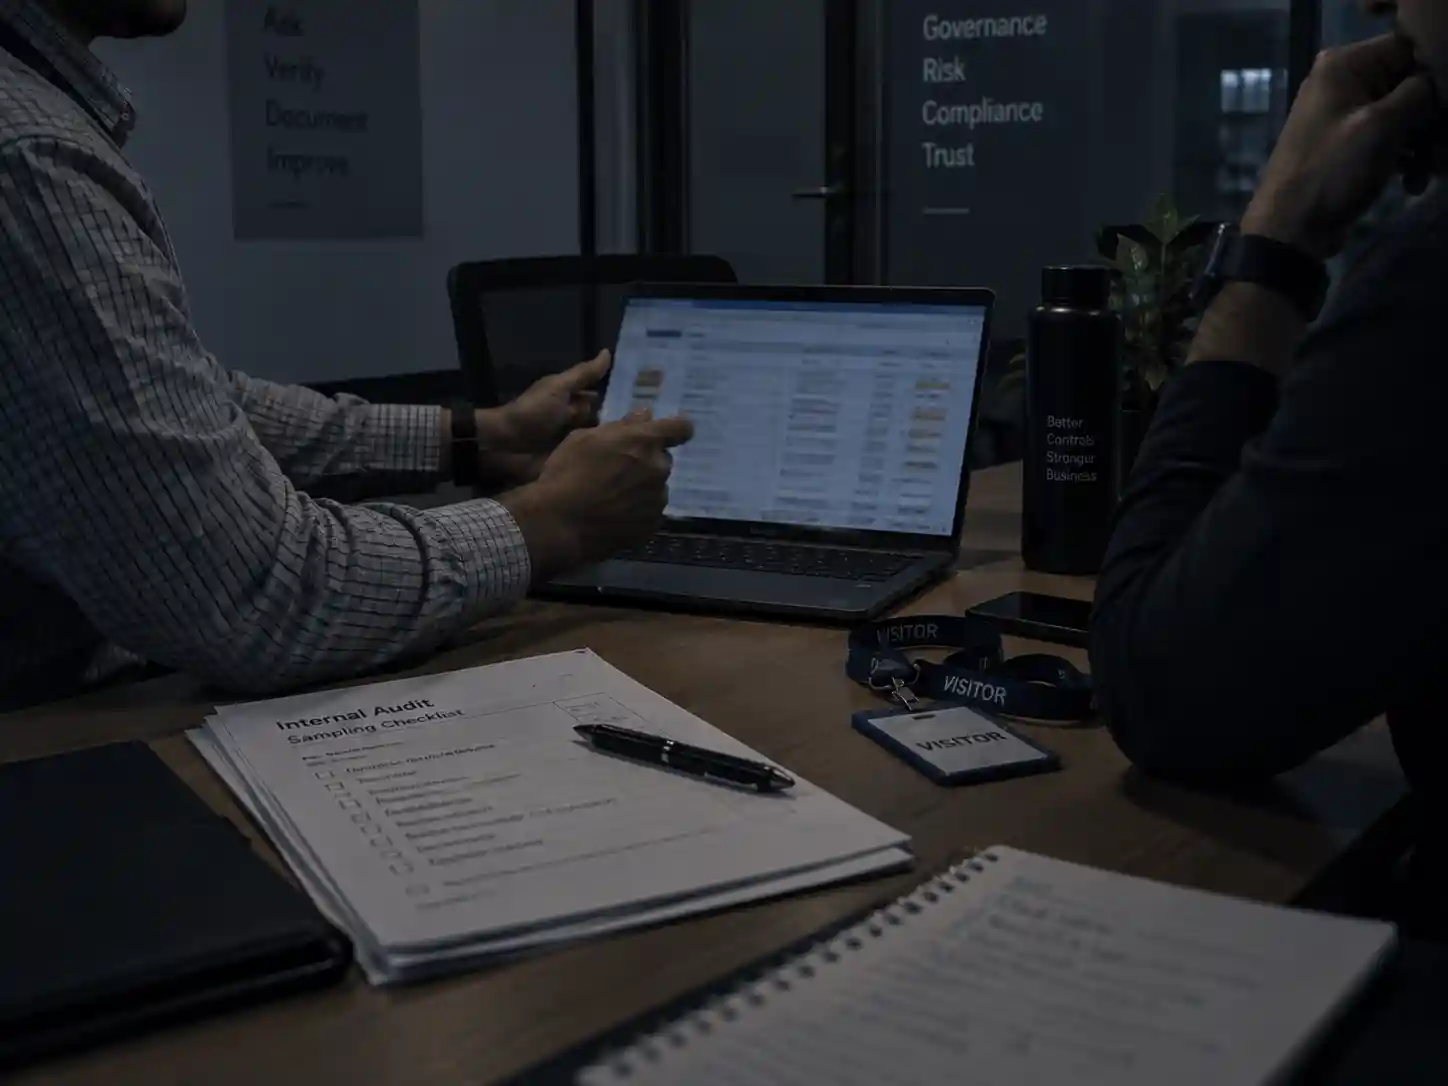
Internal audit & readiness
A full dry-run audit with evidence sampling, management review and corrective actions before the certification body arrives.
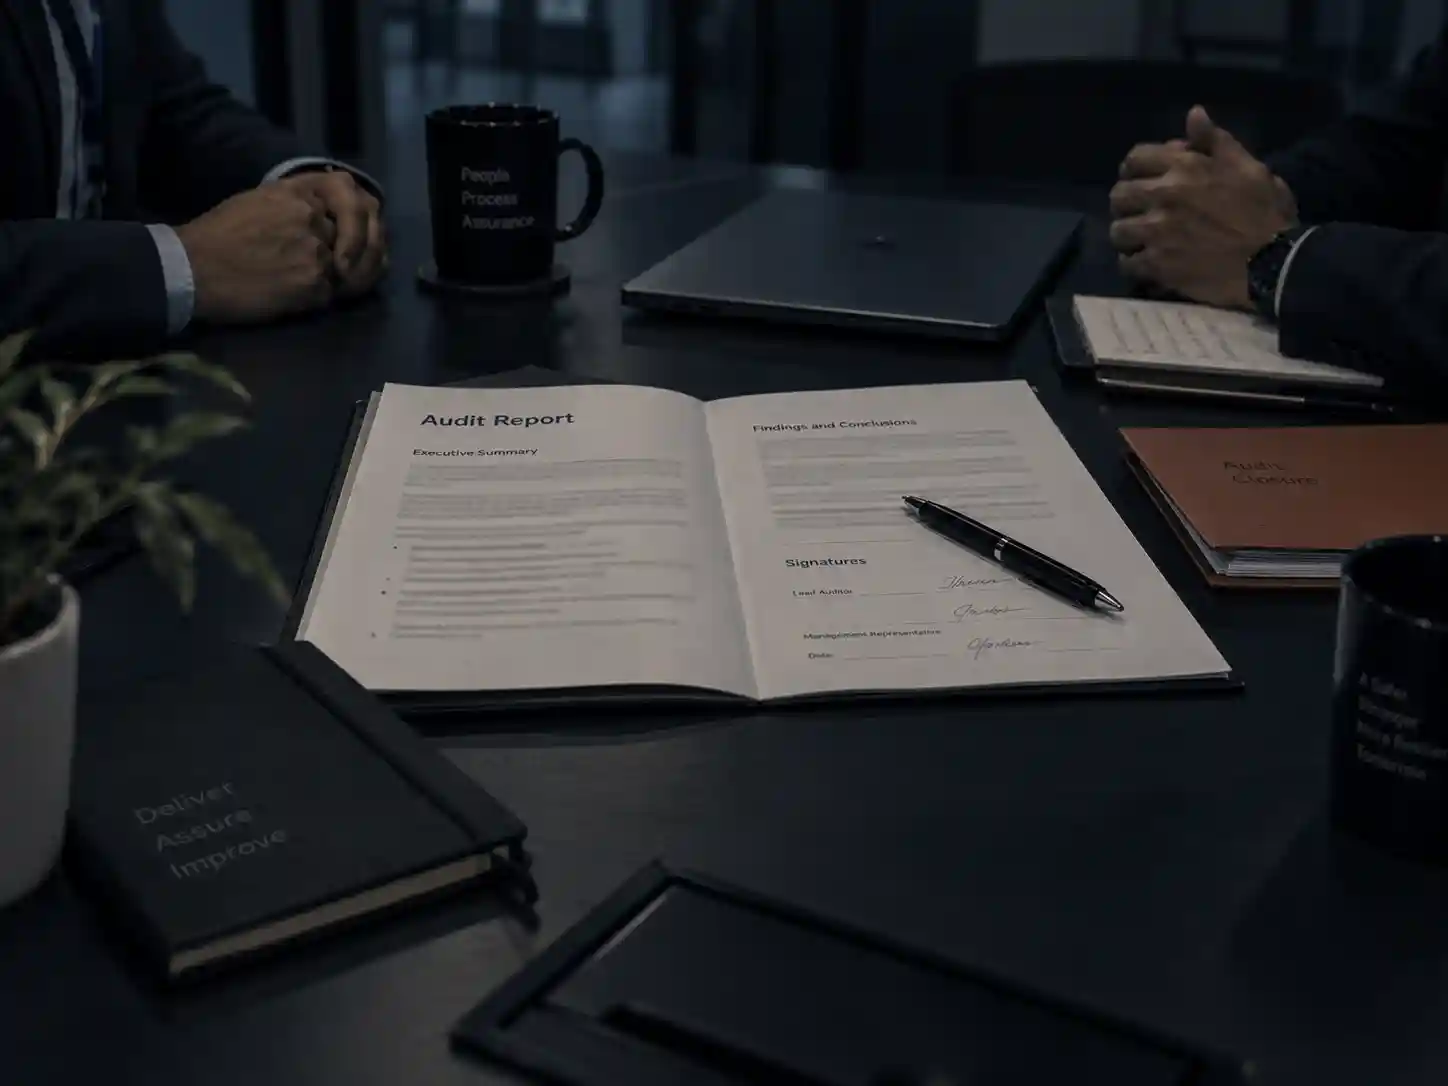
Certification & surveillance
We coordinate the accredited audit, close findings and keep you audit-ready through annual surveillance cycles.
Start where you actually are
Three ways in. Every one of them is fixed-fee, time-boxed and quoted after a free scoping call — never on a day rate that grows.
Gap assessment
Fixed fee · 2–3 weeks
- Applicability and scope analysis
- Clause-by-clause control review
- Board-ready gap report with owners
- Dated remediation roadmap
- Realistic budget and timeline
Certification programme
Fixed fee · 8–14 weeks
- Everything in the gap assessment
- Policies, procedures and risk treatment
- Implementation alongside your teams
- Internal audit and management review
- Certification body liaison to issue
Managed compliance
Annual retainer
- Surveillance audit preparation
- Quarterly internal audits
- Fractional CISO and DPO advisory
- Vendor and customer questionnaire support
- Incident response on retainer
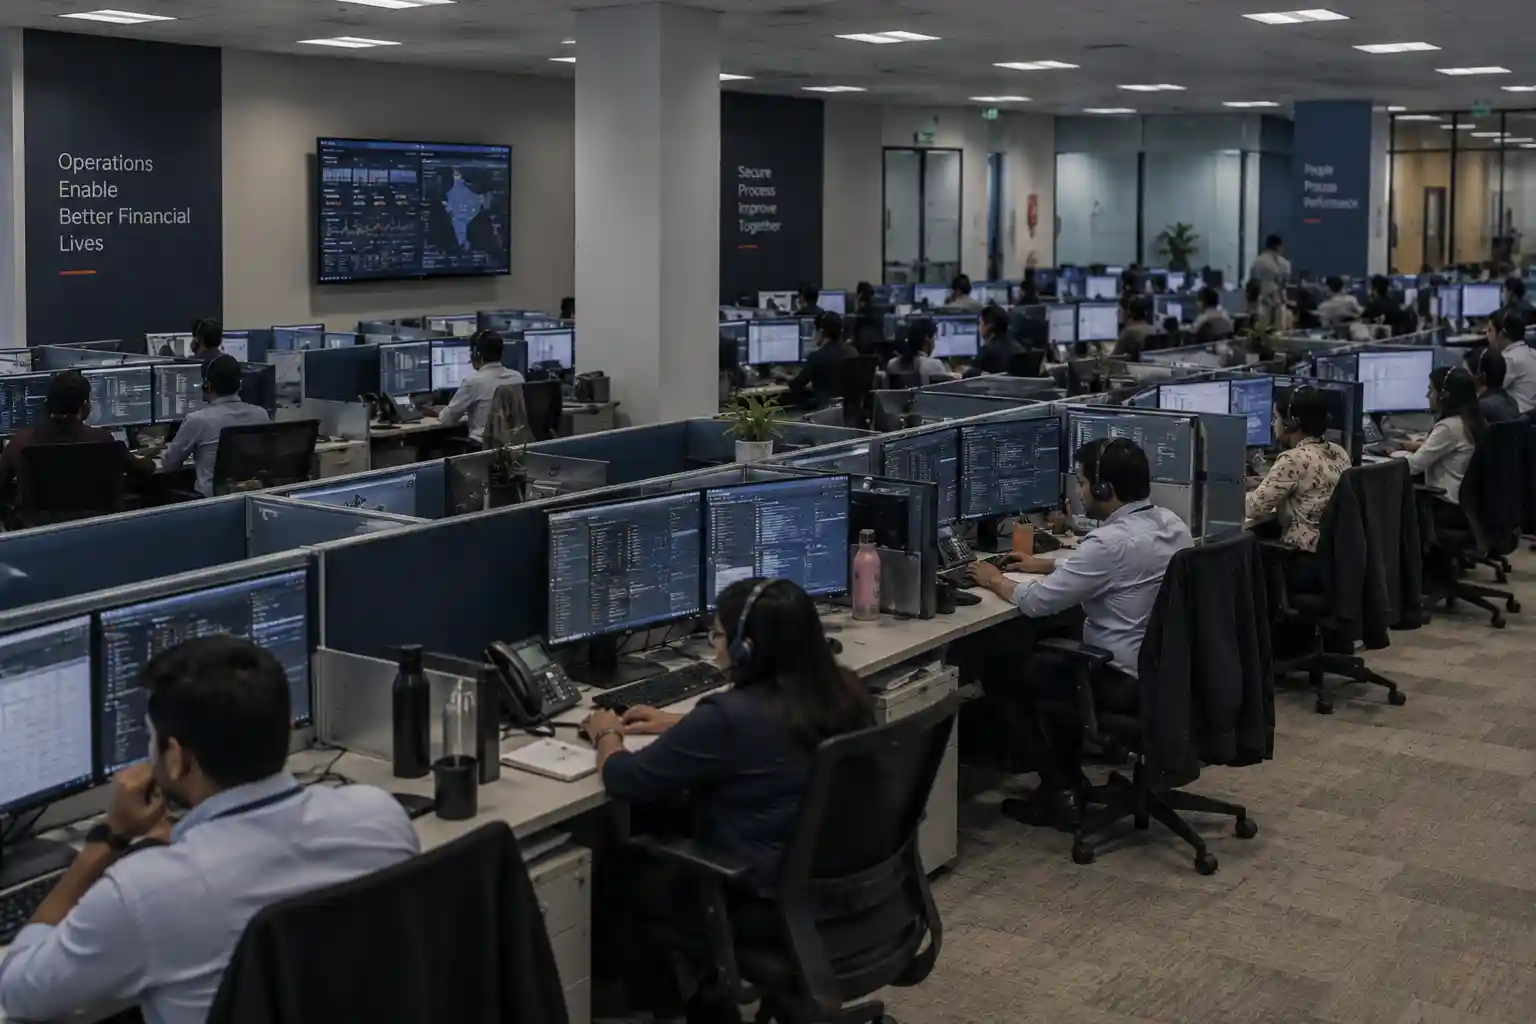
Auditors who already speak your language
A food plant, a payment aggregator and a signalling supplier fail audits for completely different reasons. We staff engagements with people who have seen yours.
Financial & Professional Services
BFSI, fintech, legal, accounting and consulting firms.
View sector
Food & Beverage
Processing, cold chain, QSR, packaging and export.
View sector
Energy & Renewables
Generation, transmission, solar, wind and storage.
View sector
Technology & Data Centres
SaaS, IT services, telecom and data centre operations.
View sector
Construction & Engineering
EPC, infrastructure, real estate and industrial projects.
View sector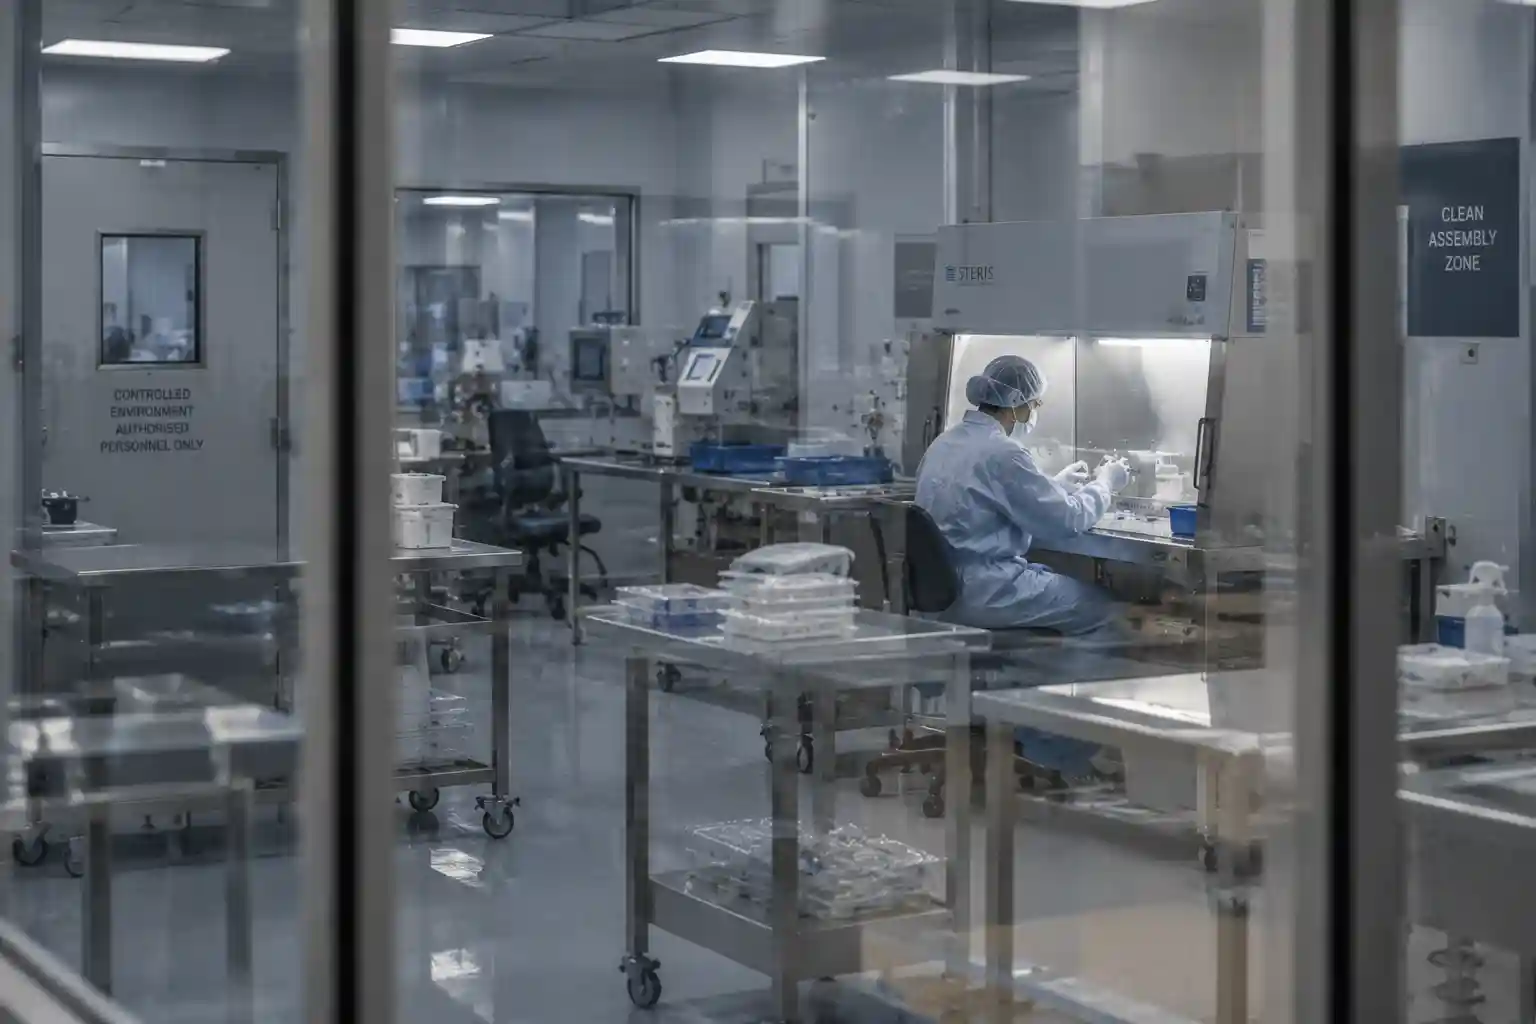
Healthcare & Medical
Hospitals, healthtech, devices, diagnostics and pharma services.
View sector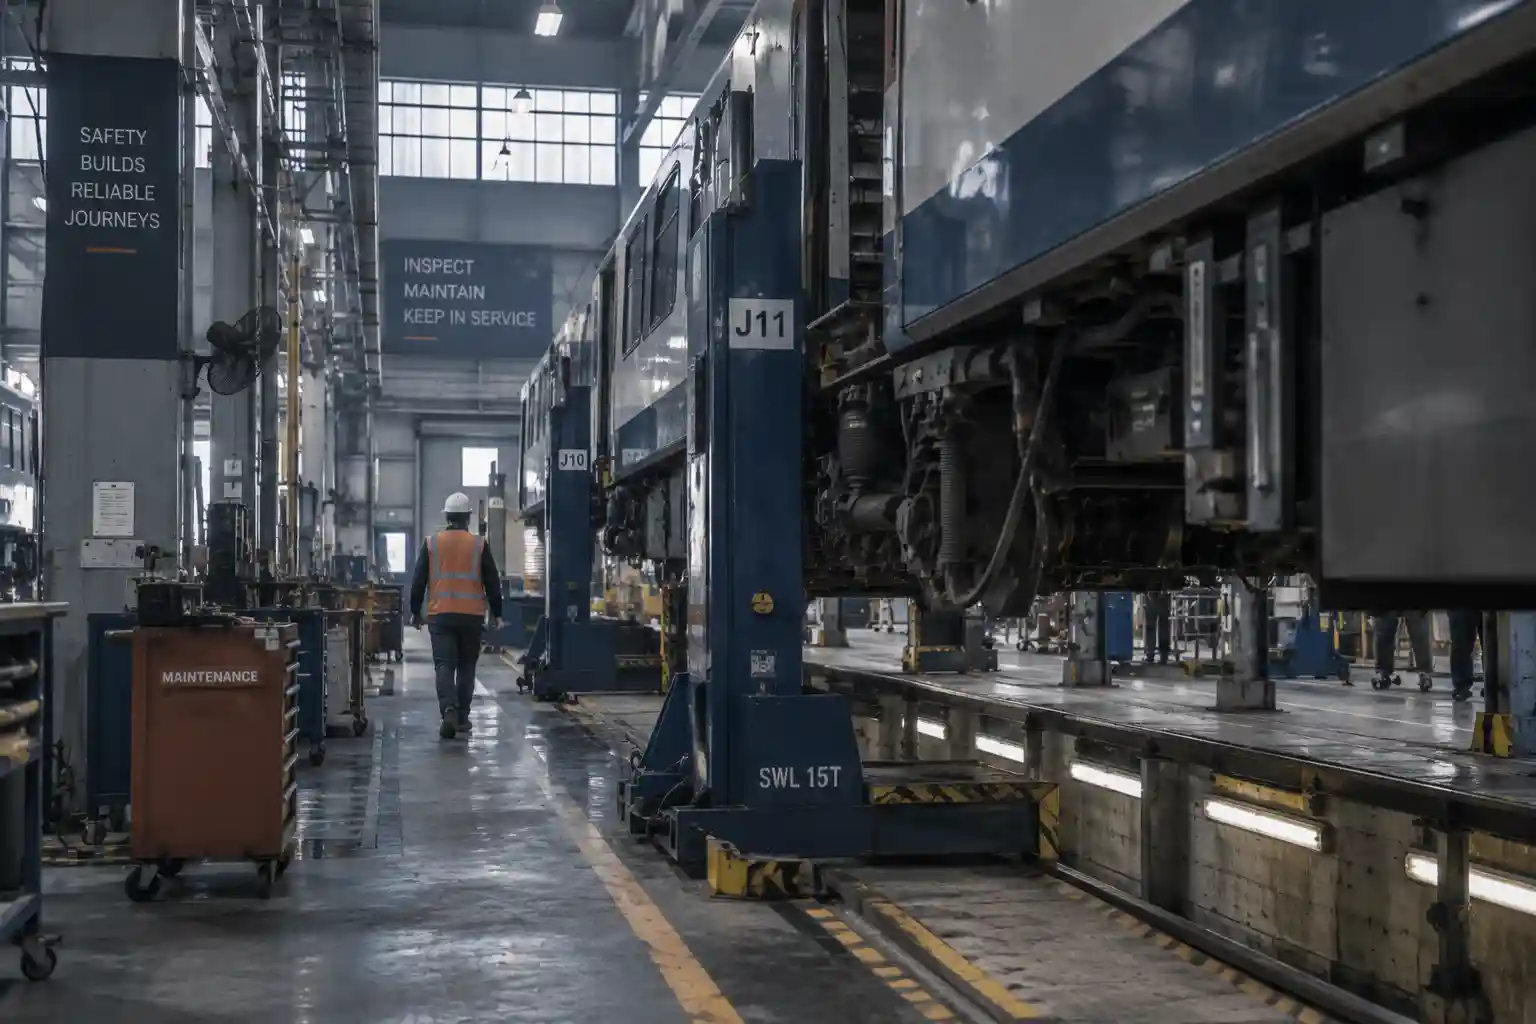
Railway Industries
Rolling stock, signalling, metro, and railway suppliers.
View sector
All other industries
Manufacturing, pharma, retail, logistics, education, government, aviation and more.
See full listWho is actually doing the work
Accreditation, empanelment and personal certifications — the things worth checking before anyone signs a compliance contract.
 NABCB accredited partners
IAF MLA recognised
CERT-In methodology
PCI DSS QSA-led
 ISO 27001 certified team
Lead auditors (IRCA / Exemplar)
Licensed CPA firm network
CMMI certified appraisers
Audited from India, accepted everywhere
Certificates issued through IAF MLA signatory bodies are recognised in more than 100 economies. We deliver remotely across 38+ countries with engagement teams in India and the UAE.
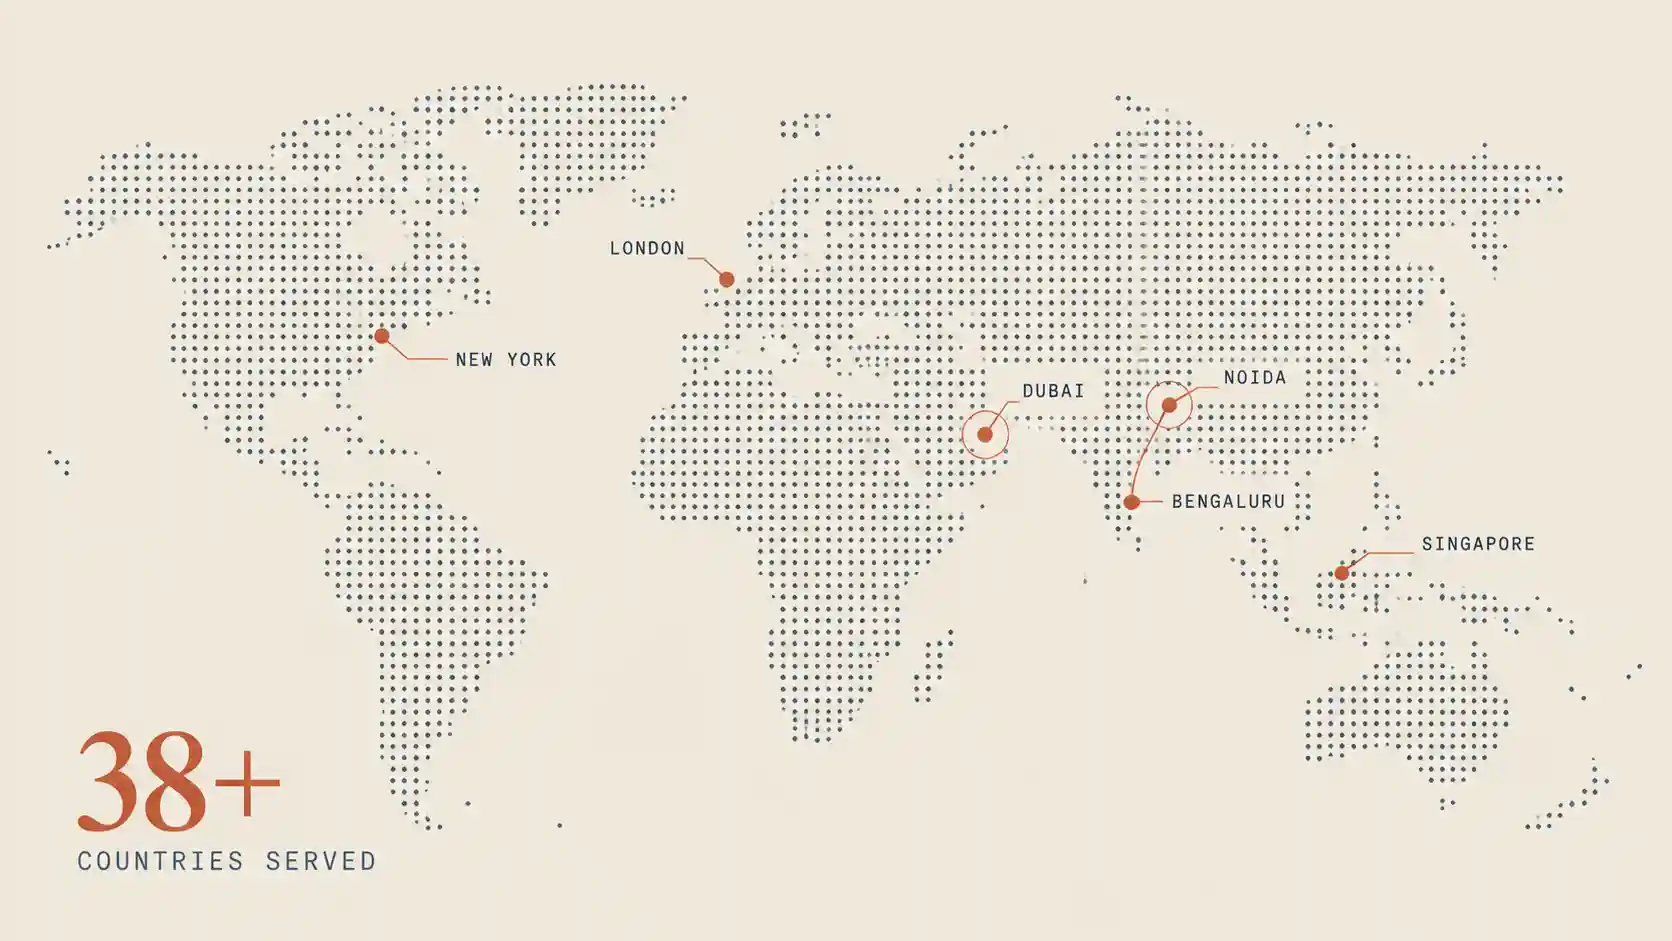
Delivery hubs in India and the UAE, remote engagement teams across 38+ countries.
What changes after certification
Questions we are asked before every engagement
Most organisations reach certification in 8 to 14 weeks. A 50-person SaaS company usually completes ISO 27001 or SOC 2 readiness in 8–10 weeks; multi-site manufacturers with several standards in scope typically need 12–20 weeks. We publish the week-by-week plan before the engagement starts.
No — and that is deliberate. Accreditation rules require independence between the consultant and the certification body. Vyapari Solutions prepares you, runs the internal audit and manages the process, while an accredited certification body or licensed CPA firm performs the final audit and issues the certificate.
No. We build one integrated control set and test shared controls once. Organisations combining ISO 27001 with SOC 2, DPDP or GDPR typically save 30–40% versus running the projects separately, and their teams answer each evidence request only once.
A complete management system: scope and applicability statement, policies and procedures, risk assessment and treatment plan, control implementation evidence, internal audit and management review records, corrective action log, and the auditor liaison through to certificate issue.
Yes. We deliver remotely across 38+ countries and hold engagement teams in India and the UAE. GDPR, HIPAA, SOC and PCI DSS work is routinely delivered for clients in the EU, UK, US, GCC and APAC.
Fixed fee per engagement, quoted after a free scoping call. The quote states the standards in scope, sites, headcount, number of audit days and every deliverable, so there are no change orders once work begins. Certification body fees are billed separately by that body.
Still not sure what applies to you?
Ask an assessor directly — we answer scoping questions before anyone talks about a fee.
Find out exactly what you need — in 30 minutes
Tell us who is asking for compliance and why. We will map the frameworks that actually apply, the realistic timeline, and a fixed fee. No proposal theatre.